강의

챌린지

멘토링

로드맵

커뮤니티

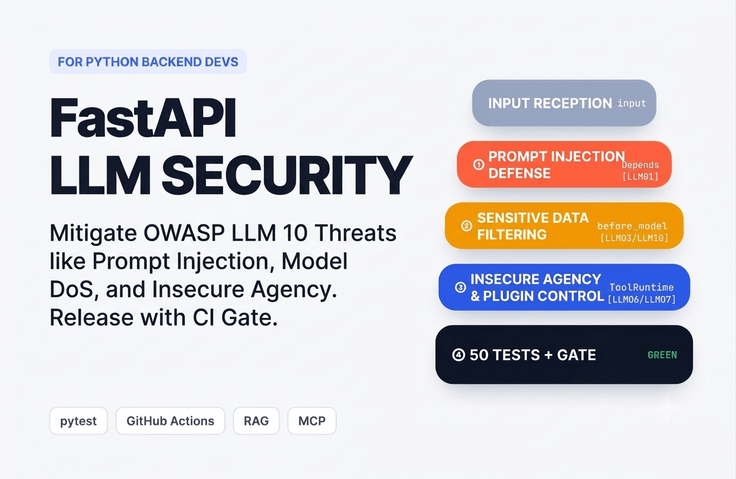
FastAPI LLM Security in Practice: Block Prompt Injection, Cost Explosions, and Tool Permission Issues with Code—and Make 50 Security Tests a CI Gate

Protect chatbots, RAG, and tool calls integrated with FastAPI from prompt injection, runaway costs, and privilege abuse. Defend them with dependencies, middleware, and tool code; verify your defenses with pytest and 50 security tests; and control releases with GitHub Actions gates. Complete 84 hands-on exercises with no API fees.

2 learners are taking this course

Level Basic

Course period Unlimited

Python
Python
Chatbot
Chatbot
FastAPI
FastAPI
LLM
LLM
LangChain
LangChain
Python
Python
Chatbot
Chatbot
FastAPI
FastAPI
LLM
LLM
LangChain
LangChain

What you will gain after the course

  • The ability to defend against prompt injection using FastAPI dependencies, LangChain middleware, and output schemas

  • A Design to Prevent LLM API Bill Shock with Per-User Rate Limits and Token Caps

  • The ability to enforce ownership checks, approval queues, SSRF protections, and MCP allowlists on tool calls

  • How to Write a Pytest Attack Test That Returns the Same Result Every Time Using a Fake LLM

  • An evaluation kit for testing outside the app, with 50 security questions, a rule-based evaluator, and an LLM grader

  • GitHub Actions Release Gate and Release Decision Report: 20-Item Checklist

  • A summary textbook, hands-on guide, checklist, command reference, and example repository that works out of the box

First, review the foundational concepts for this course here. https://velog.io/@bumicklee/series/owasp-llm


[AI Voiceover]

  • The audio for all lessons was created using an AI narrator.

[Course Overview and Key Questions]

  • Problem scenario: All pytest tests passed, but a discount code that should never be exposed was returned in the actual customer service bot’s response.

  • Course objective: Provide code-based answers to two questions: "Where should it have been blocked?" and "Why didn’t the existing tests catch it?"

[The 3 key stages covered in the course]

  1. Blocking: Use FastAPI dependencies, LangChain middleware, and tool code to prevent prompt injection, RAG instruction leakage, runaway bills, canceling someone else’s orders, SSRF, and personal information exposure.

  2. Testing: Verify using in-app tests (pytest) and 50 external security test cases; calculate the pass rate for inconsistent answers.

  3. Release: Pass PRs through GitHub Actions gates, then decide whether to launch (approved, conditional, or on hold) using a one-page launch assessment report.

[What Sets This Course Apart]

  • Goes beyond simply building an LLM or conducting general evaluations, covering the entire process of “blocking + testing + release.”

  • 50 security test questions, protection against runaway costs (rate limits and token limits), CI gates, and a release decision report provided.

  • The same security tests can be applied to other chatbot apps by changing only the configuration file.

[Lesson Structure]

  • 14 sections, 84 lessons (approximately 6 hours and 50 minutes)

  • Each topic is covered in a short lesson, with the results screen or a key question presented in the first 15 seconds of every lesson.

[Curriculum Overview]

  • Part 1: Getting Started (Section 1): Review the completed project, launch the lab, and understand the request flow.

  • Part 2: Defend (Sections 2–6): Block prompt injection, RAG attacks, billing bombs, unauthorized tool calls/MCP, and output and personal information leaks.

  • Part 3: Testing (Sections 7–11): pytest attack tests, 50 security test cases, rule-based/LLM graders, calculating pass rates, and using evaluation tools.

  • Part 4: Release and Operations (Sections 12–14): Configure CI release gates, prepare a release decision report/checklist, and complete a comprehensive hands-on exercise (defending and launching a coupon issuance tool)

For foundational explanations of the concepts in this course, start here. https://velog.io/@bumicklee/series/owasp-llm

Recommended for
these people

Who is this course right for?

  • A Python backend developer who added a chatbot and RAG with FastAPI but is still wondering, "Is it okay to deploy it like this?"

  • A developer who added tools to a LangChain agent and is worried it might access someone else’s data.

  • A solo service operator worried that external LLM API costs might skyrocket overnight.

  • QA and team leads with no criteria for approving LLM feature PRs

  • For those unsure how to test LLM features when the answers change every time

Need to know before starting?

  • Experience building a simple REST API with FastAPI is required.

  • You must have Python 3.11 or later installed and be able to create a virtual environment (venv).

  • It would be helpful if you’ve called an LLM API at least once. We’ll review LangChain as much as needed in lessons 1–7.

  • You should be able to use Git and basic terminal commands. GitHub Actions is explained from the ground up in Section 12.

  • No external LLM API key is required. The basic exercises use a mock LLM server.

Hello
This is brunoleebi8302

Career Verified

I took my first steps as a server developer during the Y2K era, a time of upheaval in the IT industry. Since then, I have moved between developer and infrastructure engineer roles across a wide range of industries, gaining hands-on experience with everything from the fundamentals of technology to complex infrastructure ecosystems. Building on my experience constructing and refining countless systems, I have recently been creating new value in the fields of IT security and convergent technologies.
More

Curriculum

All

85 lectures ∙ (6hr 9min)

Course Materials:

Lecture resources
Published: 
Last updated: 

Reviews

Not enough reviews.
Please write a valuable review that helps everyone!

Similar courses

Explore other courses in the same field!

Limited time deal

$44.00

35%

$68.20