#1 Codex × Kali Linux AI Agent Penetration Testing: From ZIP/PDF Password Cracking to Ransomware Analysis
From analyzing the encryption mechanisms of ZIP, PDF, and MS Office files to hands-on dissection of the WannaCry ransomware, master static analysis tools and GPU-accelerated cracking techniques. This is a practical, security engineering-focused course that builds incident response capabilities through the development of next-generation malware analysis pipelines using OpenAI Codex and automated report generation.
Hands-on Practice in Document Password Recovery and GPU-Accelerated Cracking Using John the Ripper, hashcat, and bkcrack
Static Analysis of the WannaCry Ransomware and In-Memory Key Recovery Based on YARA, FLOSS, capa, and Ghidra
Building a Pipeline to Automate Malware Analysis with OpenAI Codex Integration and Generate XeLaTeX Incident Reports
OFFENSIVE SECURITY & FORENSICS MASTERCLASS
#1 Codex × Kali Linux:
AI Agent Penetration Testing & Complete Malware Forensics Course
From extracting ZIP·RAR·7z hashes to a Known-Plaintext Attack that bypasses passwords using just 12 bytes, a 0-second qpdf permission bypass, hands-on ransomware simulation based on a C2 control server, and WannaCry in-memory RSA key recovery with automated Codex MCP analysis — a practical security engineering pipeline completed in 10 chapters.
SECURITY SERIES #130% Special Discount Coupon to Celebrate the Launch
Beyond manual terminal commands: a next-generation security pipeline orchestrated by the Codex AI agent
Without needing to memorize Kali Linux’s 470+ hash syntax and reverse-engineering tools, this is an active security pipeline in which the LLM directly completes everything from vulnerability identification and static analysis to report generation through a FastMCP server.
✓ One-click Kali GUI (KasmVNC) on Docker WSL2✓ Dual-track GPU (CUDA, 1 billion per second) & CPU (--fork)✓ C2 ransomware simulator & in-memory key recovery
From simple brute-force attacks to mathematical key recovery and AI-driven active penetration
End the meaningless waste of time spent guessing passwords, and develop practical analytical expertise through exploiting cryptographic vulnerabilities in file architectures and automating AI agents.
Archive encryption exploitation
기존의 수동 대입 방식
If it is long or contains special characters, it cannot be decrypted even if left running for weeks.
실전 모의해킹 파이프라인
✓bkcrack Instantly mathematically recover the internal key without a password using a 12-byte PNG header
Bypass PDF document and Office protection
기존의 수동 대입 방식
Risk of data leakage from uploading documents to paid recovery tools of unknown origin
실전 모의해킹 파이프라인
✓qpdf 0-second permission bypass & 1-second sheet protection bypass by manipulating Excel XML tags
Ransomware Response and Analysis
기존의 이론 중심 교육
Stops at the superficial warning that “ransomware is dangerous” and urging caution.
실전 모의해킹 파이프라인
✓Run the actual infection in an isolated environment and gain hands-on experience observing specific symptoms such as file encryption, C2 communication, and desktop modification.
Security Tool Control and Static Forensics
기존의 수동 대입 방식
Manually compile the results of YARA, Ghidra, capa, and FLOSS commands one by one
실전 모의해킹 파이프라인
✓Automated PE structure analysis, IOC extraction, and PDF report generation through Codex integration based on FastMCP
Docker-based one-click isolated environment setup for Kali Linux
ONE-CLICK DOCKER SETUP
There is no need for complex dual-boot setups or purchasing a separate physical machine dedicated to hacking. We provide a 100% isolated and secure practice environment by running a KasmVNC-based Kali Linux GUI container on Windows WSL2, accessible directly through a web browser (`localhost:3001`).
One-click automatic installation script
Batch setup of John, hashcat, bkcrack, YARA, and Ghidra with install_kali_final.sh
NVIDIA CUDA GPU acceleration
Ultra-fast cracking of 1 billion hashes per second using the host GPU via WSL2 driver passthrough
CPU Multicore Dual Track
Even without an external GPU, practice comfortably on a laptop using the john --fork=$(nproc) parallelization technique.
Attack & Forensics Showcase
Key Practical Attack & Forensics Takeaways by Chapter
These are the hands-on attack scenarios configured and executed directly in the course, along with recovery and analysis demo results.
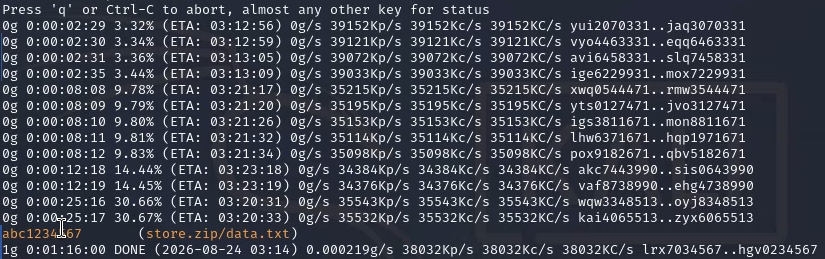
CH 02-03 · GPU & CPU Cracking
John the Ripper vs Hashcat: Ultra-Fast Parallel Hash Cracking for 470+ Formats
A hands-on demo screen showing the extraction of header-verification hashes from ZIP (PKZIP/AES), RAR5, and 7-Zip archives, and the ultra-fast recovery of complex passwords through GPU CUDA acceleration and CPU --fork multicore parallelization.
zip2johnhashcat CUDArockyou.txt--fork multicore
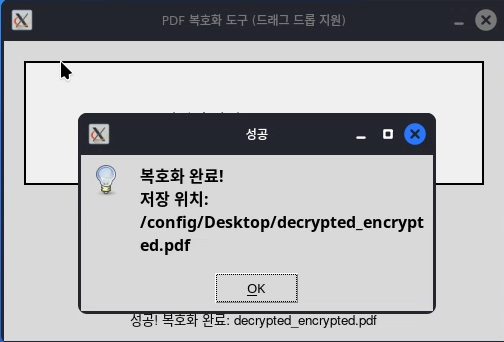
CH 05 · PDF GUI Tool
PDF Document Security Analysis & Drag-and-Drop Permission Bypass GUI Tool Development
This is the completed result: it identifies the structural differences between the User Open password and the Owner Permissions password, and combines qpdf’s core decryption logic with Python’s pikepdf and Tkinter to create a GUI utility that removes printing and copying restrictions in 0 seconds when a file is dragged and dropped.
qpdf --decryptpikepdfTkinter GUIPermissions removed in 0 seconds
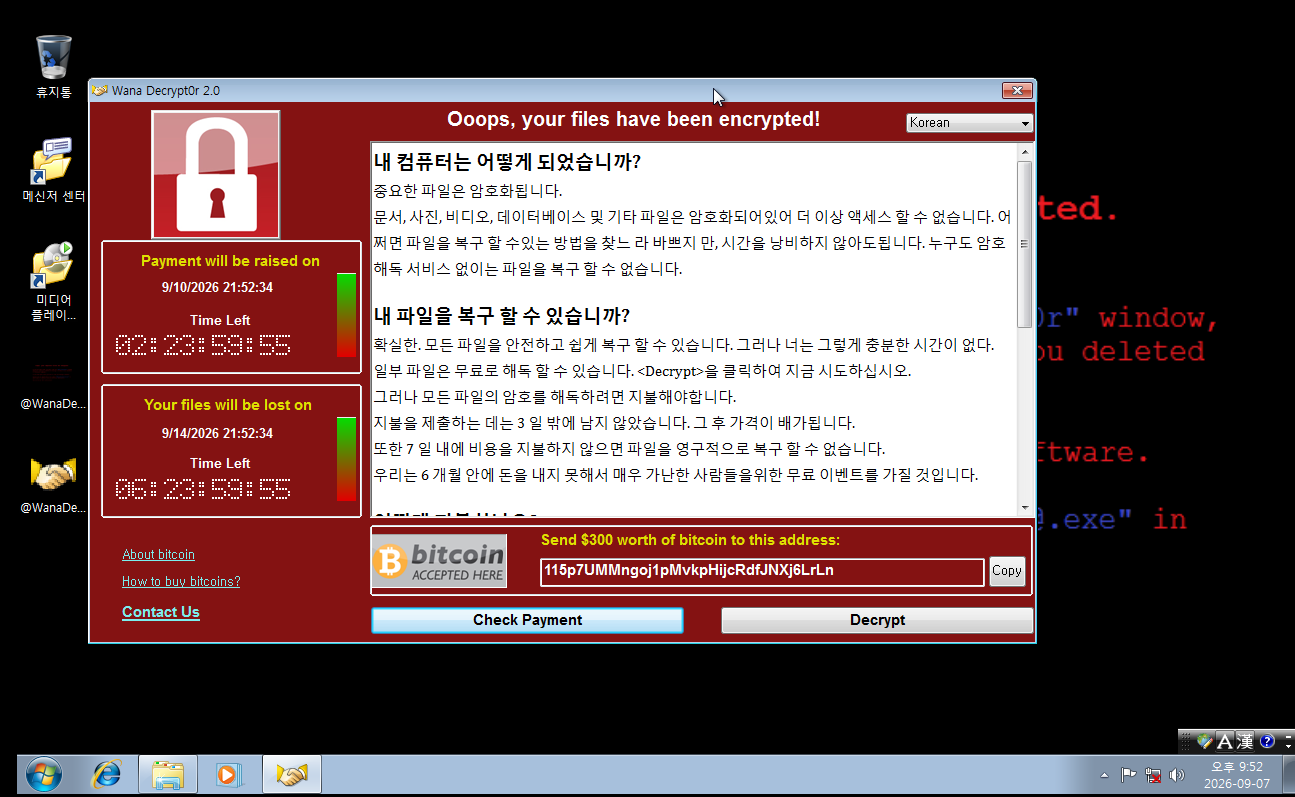
This hands-on exercise result involves executing the actual WannaCry ransomware in a secure, isolated virtual machine environment to directly experience and analyze the symptoms of a real cyberattack: all file extensions are forcibly encrypted to .WNCRY, a Bitcoin ransom demand window appears, and the desktop is altered with a red warning.
Experience real infection symptomsReal-time file encryptionForced desktop modificationIsolated VM analysis environment
CH 09 · WannaCry Forensics
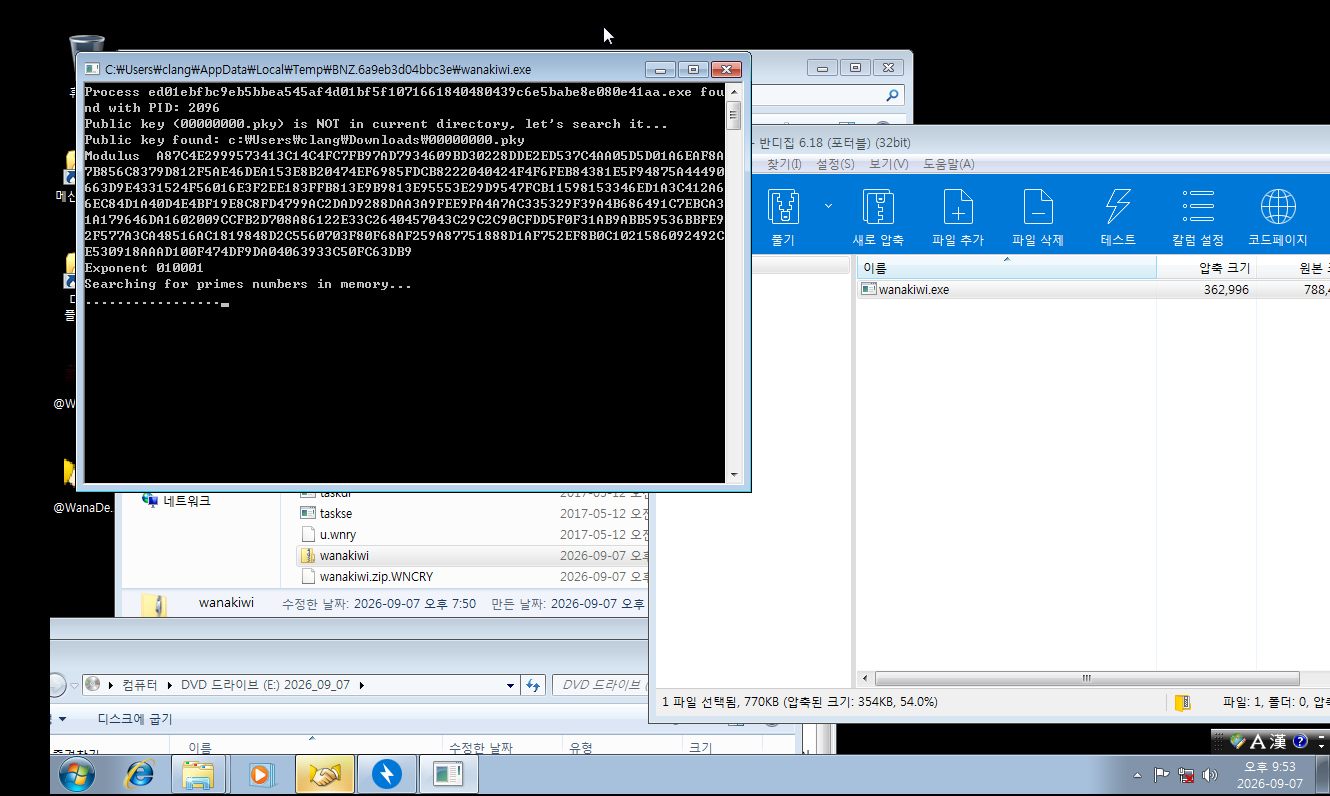
WannaCry In-Memory Forensics: Reconstructing the RSA Private Key and Recovering Files Using wanakiwi
This is a hands-on memory forensics screen demonstrating how, after a WannaCry infection in an isolated Windows virtual machine environment, the prime numbers p and q remaining in the process memory heap are scanned and extracted in real time to reconstruct the RSA-2048 private key and fully restore the .WNCRY-encrypted files to their original state.
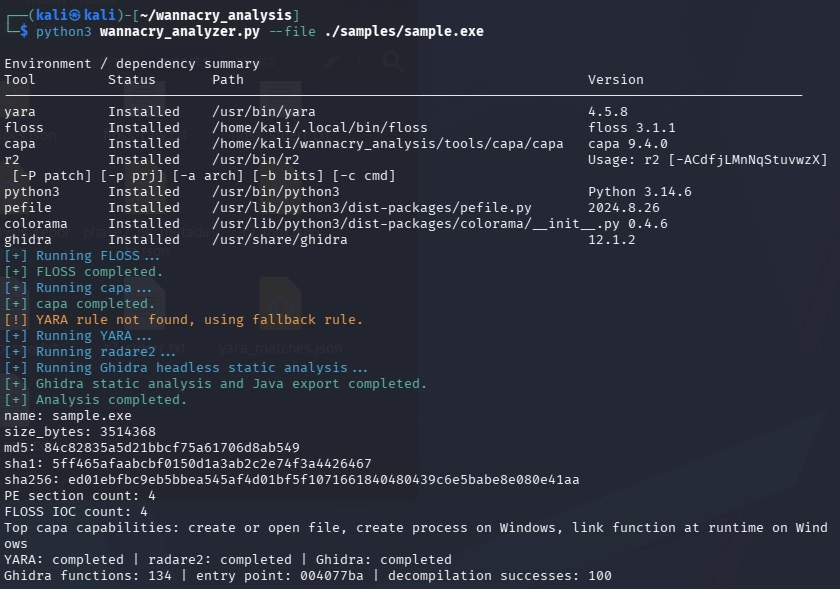
Kali Linux Professional Analysis Toolchain Integration: WannaCry Sample Analysis & Automatic Generation of a Codex Incident Response Report
By integrating a professional static and dynamic analysis toolchain—including YARA, FLOSS, capa, radare2, and Ghidra Headless—built on Kali Linux into a pipeline, we perform an in-depth analysis of the WannaCry executable sample file (sample.exe) and automatically generate a professional security report consolidating indicators of compromise (IOCs) and function decompilation results through the OpenAI Codex AI agent.
Kali Linux Analysis ToolchainGhidra Headless & capaIn-Depth Analysis of the WannaCry SampleAutomated Codex Report Generation
Curriculum Breakdown
Detailed Curriculum for All 10 Chapters
It consists of a total of 51 detailed lessons.
Source code and toolkits for all chapters provided: You can download the install_kali_final.sh automated installation script, the RansomwareSim C2 simulator, the FastMCP security tool server, and a complete set of automated analysis report templates!
CH 00Orientation & Core Principles of EncryptionWhite-Hat Hacker Ethics
4 Lessons
0-1Course Introduction and Complete Hands-On Practice Roadmap Guide
0-2Prerequisite Knowledge and Recommended Hardware Specifications Virtualization extensions VT-x/AMD-V required
0-3[Required Reading] 2026 Amendment to the Information and Communications Network Act and White Hat Hacker Code of Ethics Legal Responsibilities & 10 Ethical Principles
0-4[PPT Theory] Core Architecture of File Encryption (Comprehensive Review of Symmetric Keys, Public Keys, KDFs, and the History of Cryptography)
CH 01Setting up a Docker-based Kali Linux environment & batch tool configurationOne-click Docker
3 Lessons
1-1Install Docker Desktop in a Windows WSL2 environment & run a Kali Linux GUI container KasmVNC localhost:3001
1-2Web browser GUI access and an automated script for batch installation of essential tools (install_kali_final.sh)
1-3Verifying proper operation for each tool, troubleshooting the 7z2john Perl library (LZMA) & extracting rockyou.txt
CH 02John the Ripper: CPU-Based Archive Cracking FundamentalsCPU Cracking
5 Lessons
2-1John the Ripper Operating Principles and Analysis of the Structure Supporting 470+ Hash Formats
2-2ZIP File Hash Extraction and Format Analysis (zip2john Practice)
Hello! I am a graduate of Sogang University's Computer Science and Engineering department, and I am currently preparing for graduate school.
I fell in love with programming in high school when I happened to start full-stack web development and automated trading using Python.
Since then, I have shared my skills and know-how through various projects and programming tutoring activities. Based on these experiences, I am striving to create lectures that make even those new to programming feel, "Wow, this can be so easy!"
I want to help you learn through practical examples and friendly explanations. Thank you.