Hacking as a Hobby #2 (Hacker's Computing)
caliber50
$26.40
29%
$18.70Beginner / Penetration Testing
4.8
(55)
1,200+
You can now enjoy more freedom in cyberspace than ever before.
Beginner
Penetration Testing
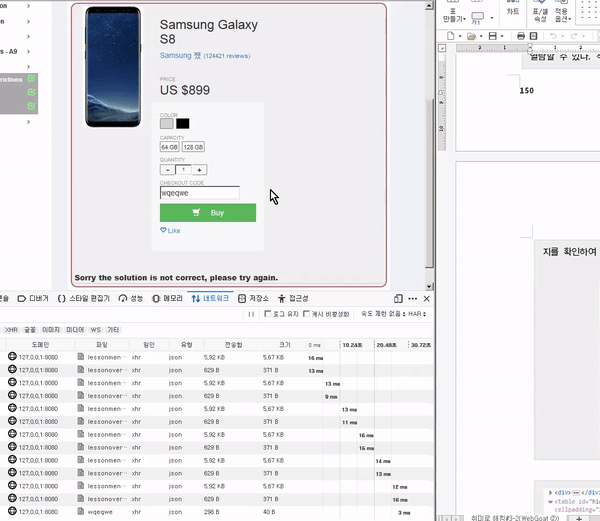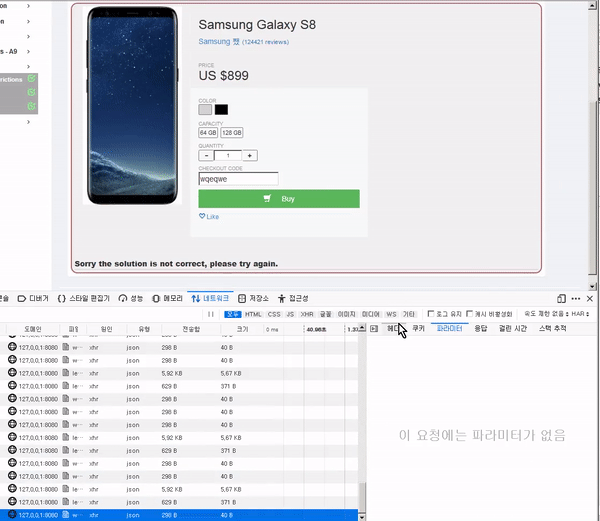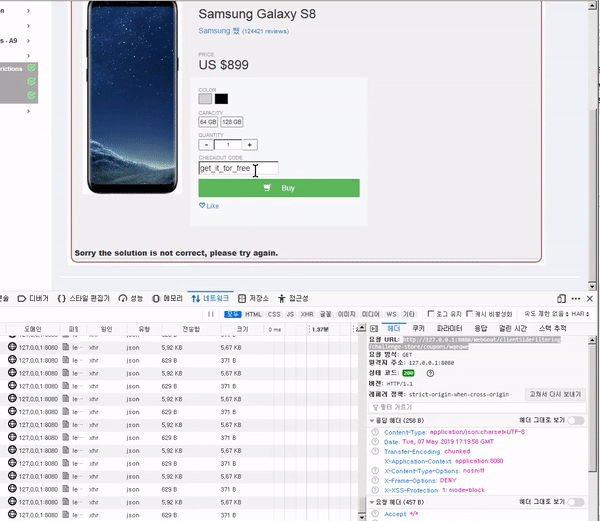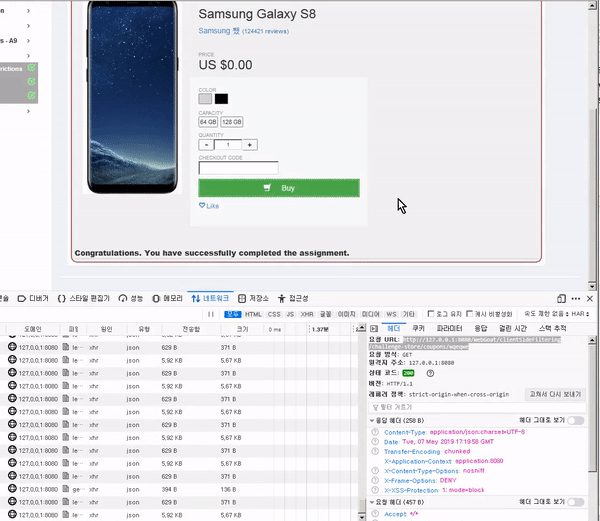
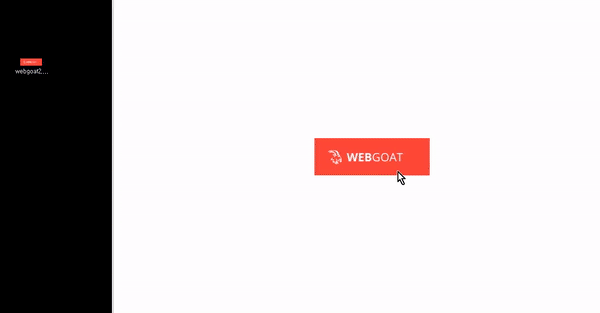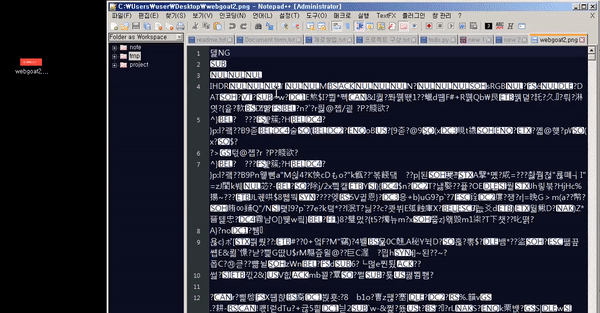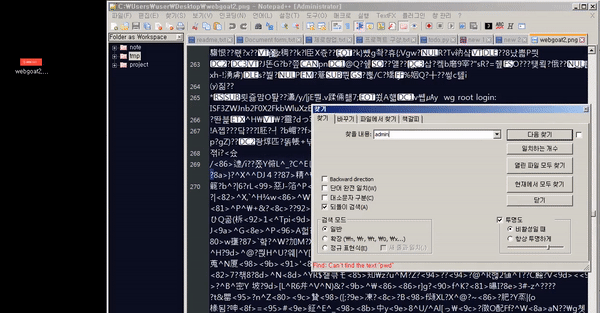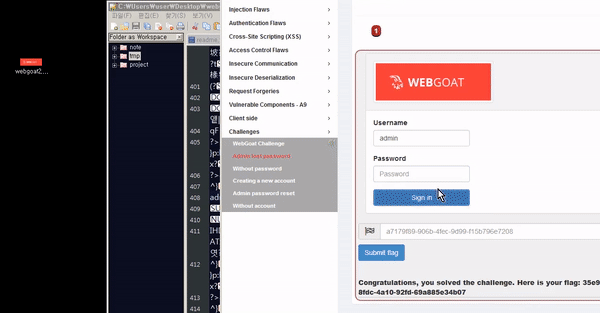
Covering the content of WebGoat, a classic web hacking wargame, this resource includes full translations and solutions for every lesson and challenge from start to finish. It provides everything from setting up the practice environment to the tools and data required to solve the challenges.
633 learners
Level Basic
Course period Unlimited


Reviews from Early Learners
5.0
김진호
Honestly, this is Hyeja. There is a place that offers a 5-day lecture through Webgoo, but they charge 150,000 won per person without even finishing the course. ㅂㄷㅂㄷ...
5.0
이지혁
Honestly, I thought I would be satisfied with just learning SQL injection, but there were many unexpected contents, and they were explained kindly, so I was able to learn easily even though there was a lot of content. It doesn't just pick out the easy parts, but really includes all the contents. It even solves problems with real bugs...
5.0
문대현
It's fun Easy and well explained!
Ability and intuition for discovering web application vulnerabilities based on the OWASP Top 10.
Computer science knowledge related to each challenge.
Hacking as a hobby, hobbyist hacking.
※ The "Hacking as a Hobby" content aims only for legal hacking to contribute to a safe information security ecosystem.
< To view the course content as a book: Paperback/E-book (Link) >
Here, we will master WebGoat, the classic wargame of web hacking. Based on fully translated Korean materials, we will follow every lesson from start to finish and practice the challenges.
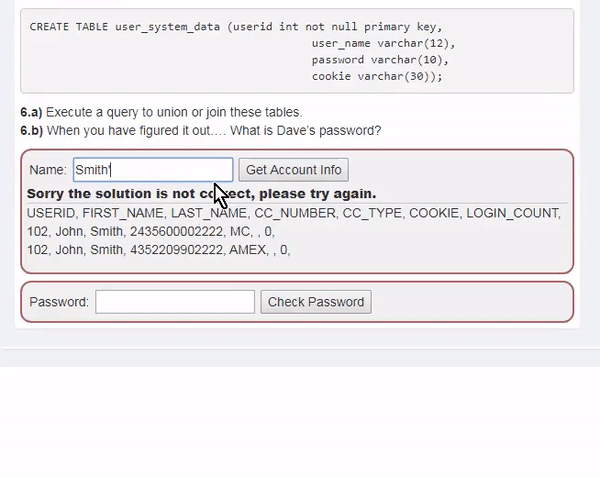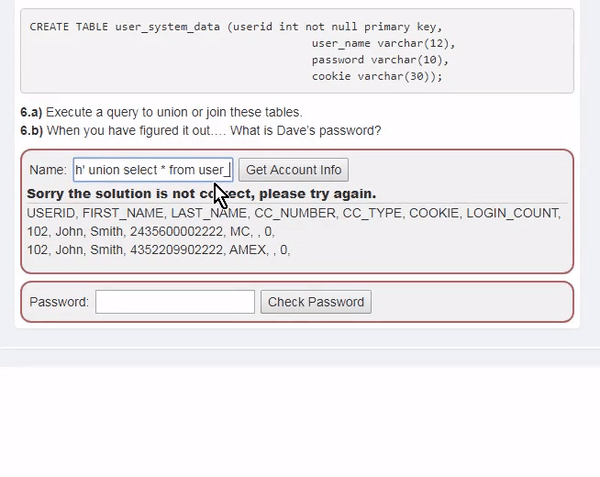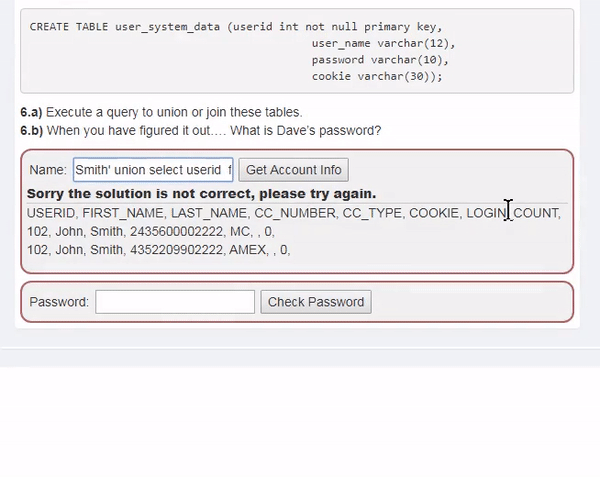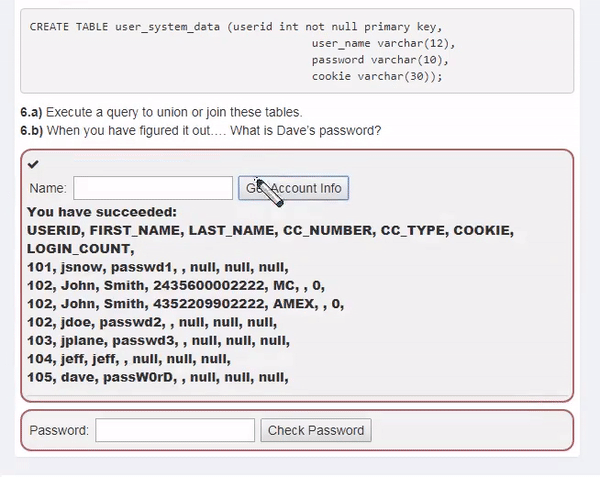
You will encounter the parts hidden beneath the areas visible through a web browser. We will intercept and manipulate communication data and request somewhat special information from the server. We will also access private pages that are inaccessible to ordinary users. We will extract other people's personal information stored in the database as if it were a matter of course. We will even try to deceive other users through the website.
Through this, you will learn how to discover and remediate various web-related security vulnerabilities. More specifically, it includes theory and practice on vulnerabilities related to SQLI, XXE, Authentication Bypass, JWT, XSS, IDOR, Access Control, Deserialization, CSRF, Vulnerable Components, Password Reset, and HTML Tampering.
To reduce any inconvenience, we will set up the practice environment together, and all tools and data required to solve the challenges will be provided.
|
|
|
|
[Q1] Which version of WebGoat is used?
[Ans] We use the M24 version, which has OWASP 2017 applied.
[Q2] I haven't taken "Hacking as a Hobby #1~2". Is it okay to start with this one?
[Ans] Yes, that is not a problem. #2 is a course focused on an overall experience related to hacking, and #1 is a course related to system hacking. Since #3 is a course corresponding to web hacking, there is low direct relevance. However, since #5, which covers participating in actual hacking competitions, deals with broader areas including systems and the web, the previous courses will not be meaningless.
[Q3] What skills will I acquire upon completing the course?
[Ans] A website developed by a novice developer who doesn't know security might look like a toy to you. However, please note that the content covered here is not the entirety of web hacking. It is at a level where you can utilize several skills based on major vulnerabilities. Now, you will finally be able to do something on your own.
Who is this course right for?
Those who want to complete all the content of the WebGoat wargame.
Those who want to learn hacking little by little as an academic hobby.
Those who wish to participate in domestic or international hacking competitions in the future.
Students in related departments who need to supplement their major knowledge.
Those who are aspiring to a career in information security.
Need to know before starting?
It can be helpful if you have experience writing Java programs.
Career Verified
12,370
Learners
1,087
Reviews
119
Answers
4.7
Rating
9
Courses
Prop Trader (Darwinex Zero, Current)
Information Security Staff Member at Hankuk University of Foreign Studies
Missile Strategic Command CERT Team Leader
Bachelor’s degree in Computer Engineering from Korea Polytechnic University (4.42)
Published over twenty books, including 『생활코딩! 파이썬』, 『취미로 해킹』, and 『취미로 투자』.
Information Security Engineer
All
62 lectures ∙ (10hr 2min)
1. 1. Prologue
03:01
5. 5. General(1)
07:46
6. 6. General(2)
07:33
7. 7. General(3)
10:27
18. 18. XXE(1)
10:32
19. 19. XXE(2)
10:02
20. 20. XXE(3)
12:56
21. 21. XXE(4)
12:38
22. 22. XXE(5)
06:11
All
26 reviews
4.7
26 reviews
Reviews 9
∙
Average Rating 4.9
Reviews 93
∙
Average Rating 4.5
Reviews 1
∙
Average Rating 5.0
Reviews 1
∙
Average Rating 5.0
5
Honestly, I thought I would be satisfied with just learning SQL injection, but there were many unexpected contents, and they were explained kindly, so I was able to learn easily even though there was a lot of content. It doesn't just pick out the easy parts, but really includes all the contents. It even solves problems with real bugs...
Reviews 10
∙
Average Rating 2.9
3
The explanation is neat and good. But I recommend that only beginners (at least those who have heard of injection) take the course. And the copyright belongs to me~~ You are responsible for any misuse~~~ etc. It is annoying that they insert it at the beginning of every clip so that people skip it even though they only need to say it once in the first lecture.
Check out other courses by the instructor!
Explore other courses in the same field!
Limited time deal ends in 1 days
$824,015.00
28%
$42.90