[Eduwill White Hacker Training Course] Network Theory
eduwill
$59.40
Basic / Network
4.7
(7)
We introduce the basic knowledge of Hack&Hat analysis, a must-have subject to become a security expert.

Basic
Network

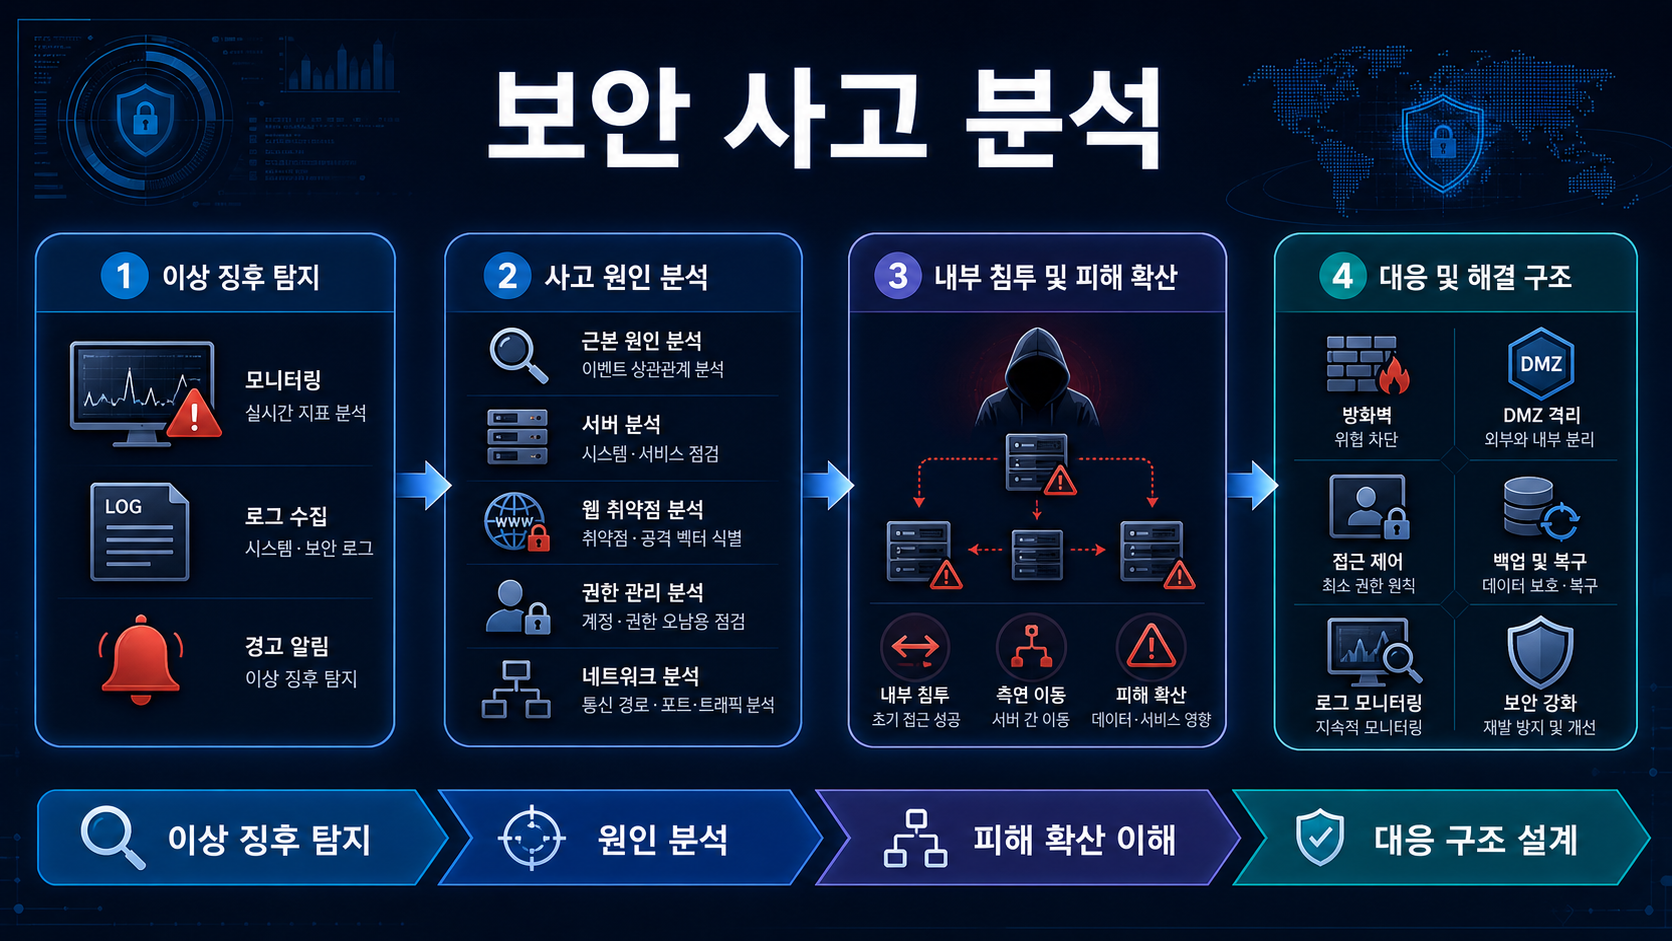
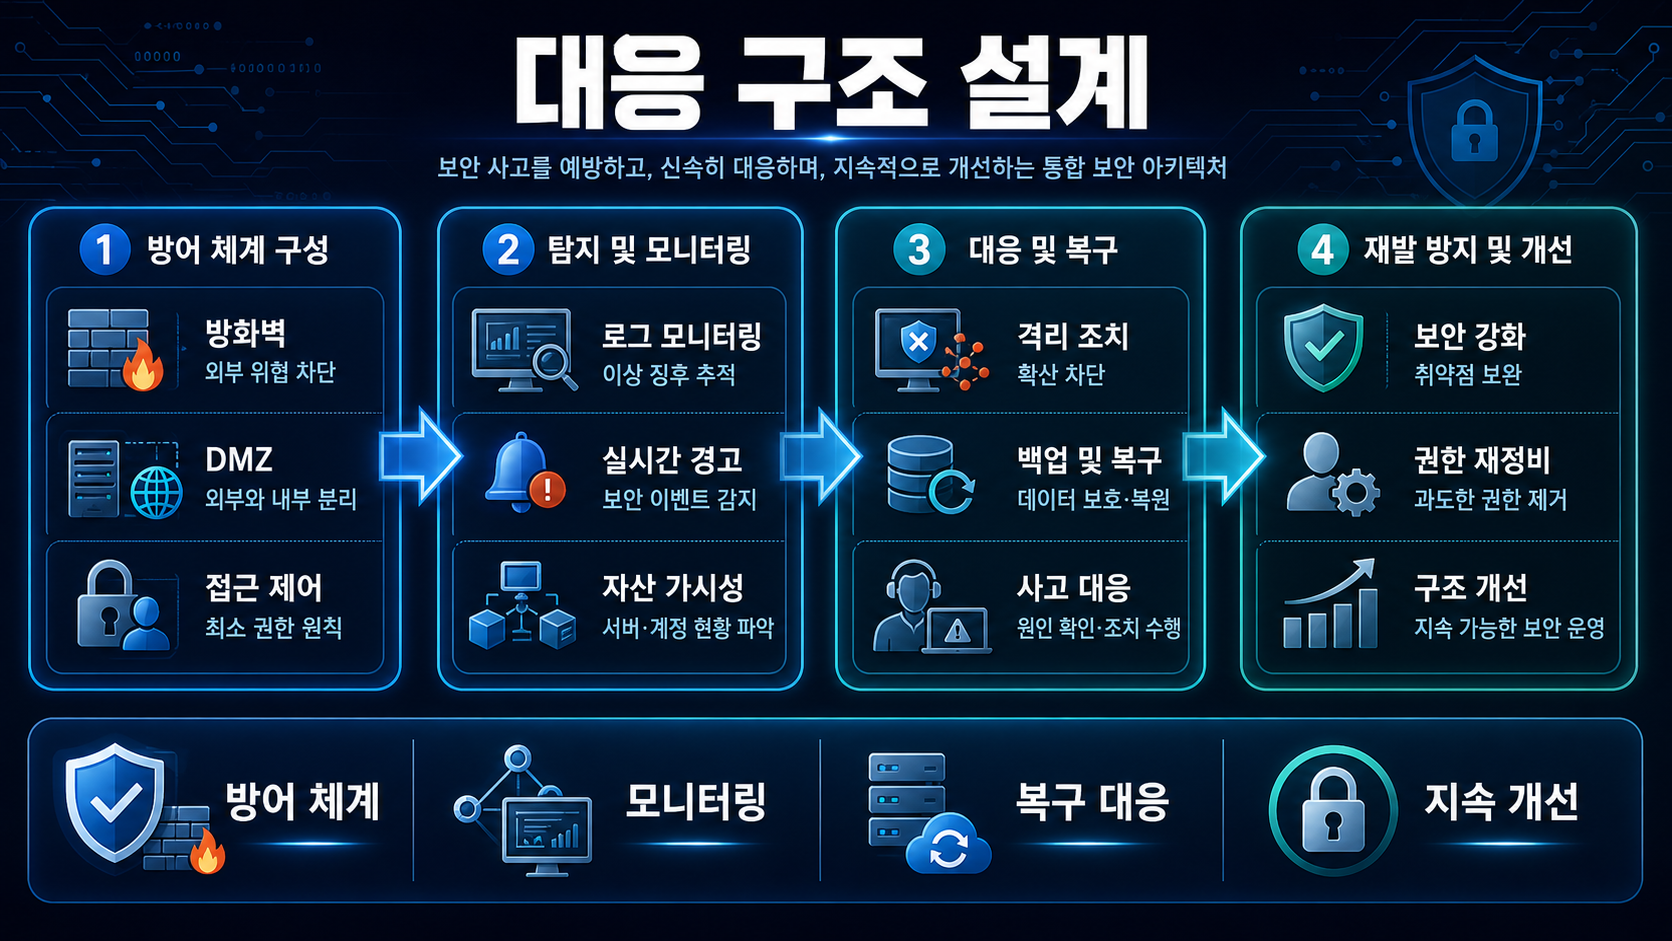
[Introduction to Security Incident Response: Learning through Scenarios of Web Server Hacking, Ransomware, and Account Takeover] This course examines why various information security incidents—such as web server hacking, ransomware, account takeover, and internal penetration—occur and how they spread, categorized by incident type. Students will follow each incident scenario to understand the attack flow, analyze the core causes of the incident, and learn how to resolve issues and prevent recurrence through security architectures such as firewalls, DMZ, access control, privilege management, backup, and log monitoring. Rather than a simple explanation of security concepts, this is a scenario-based introduction to information security that provides a comprehensive understanding from root cause analysis to resolution strategies.
18 learners
Level Beginner
Course period 12 months
Reviews from Early Learners
5.0
오명환
Good
5.0
sunny75
===== 26/06/03/Wed 13:35 ===== I have gained a great understanding of security through the lectures categorized by information security types. Thank you for creating such a great course.
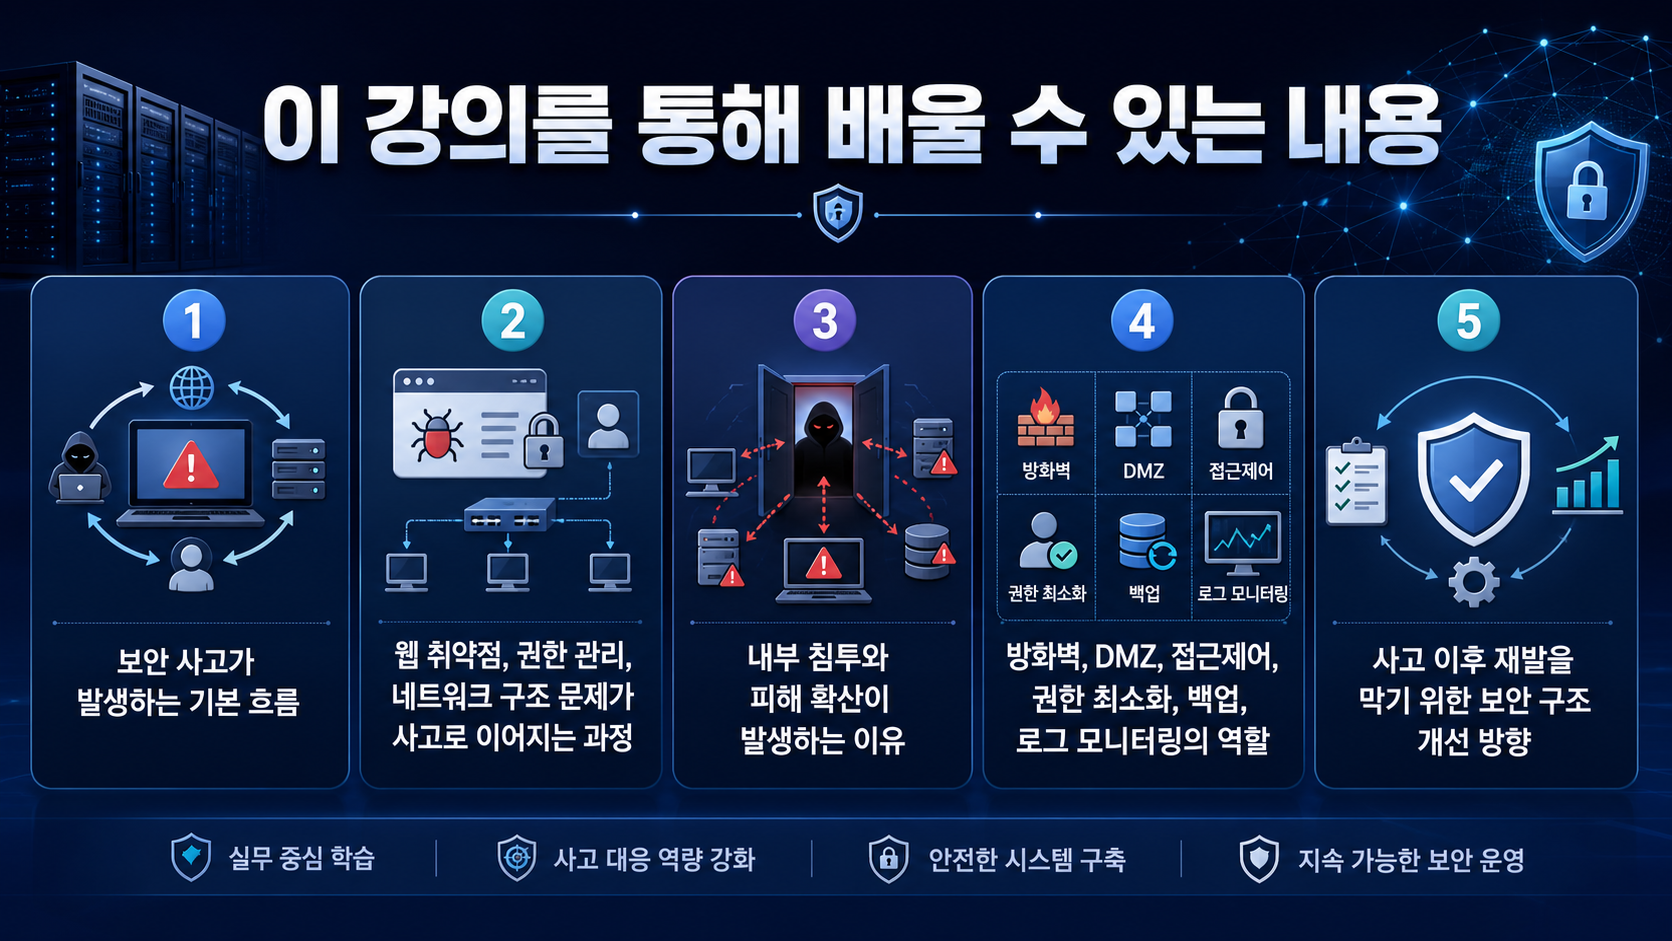
Understanding the flow of information security incidents
Identifying key causes by accident type
Understanding internal penetration and the structure of damage propagation
Learning the direction of security incident response
Understanding security architecture to prevent recurrence
In this course, you will learn by incident type how information security incidents occur, why they spread to internal systems, and how to resolve them and prevent recurrence.
By following scenarios of representative security incidents such as web server hacking, ransomware, account hijacking, internal infiltration, and data breaches, you will go beyond simply learning "what is dangerous" and gain a comprehensive understanding of the cause of the incident → process of spread → response methods → security architecture → directions for improvement.
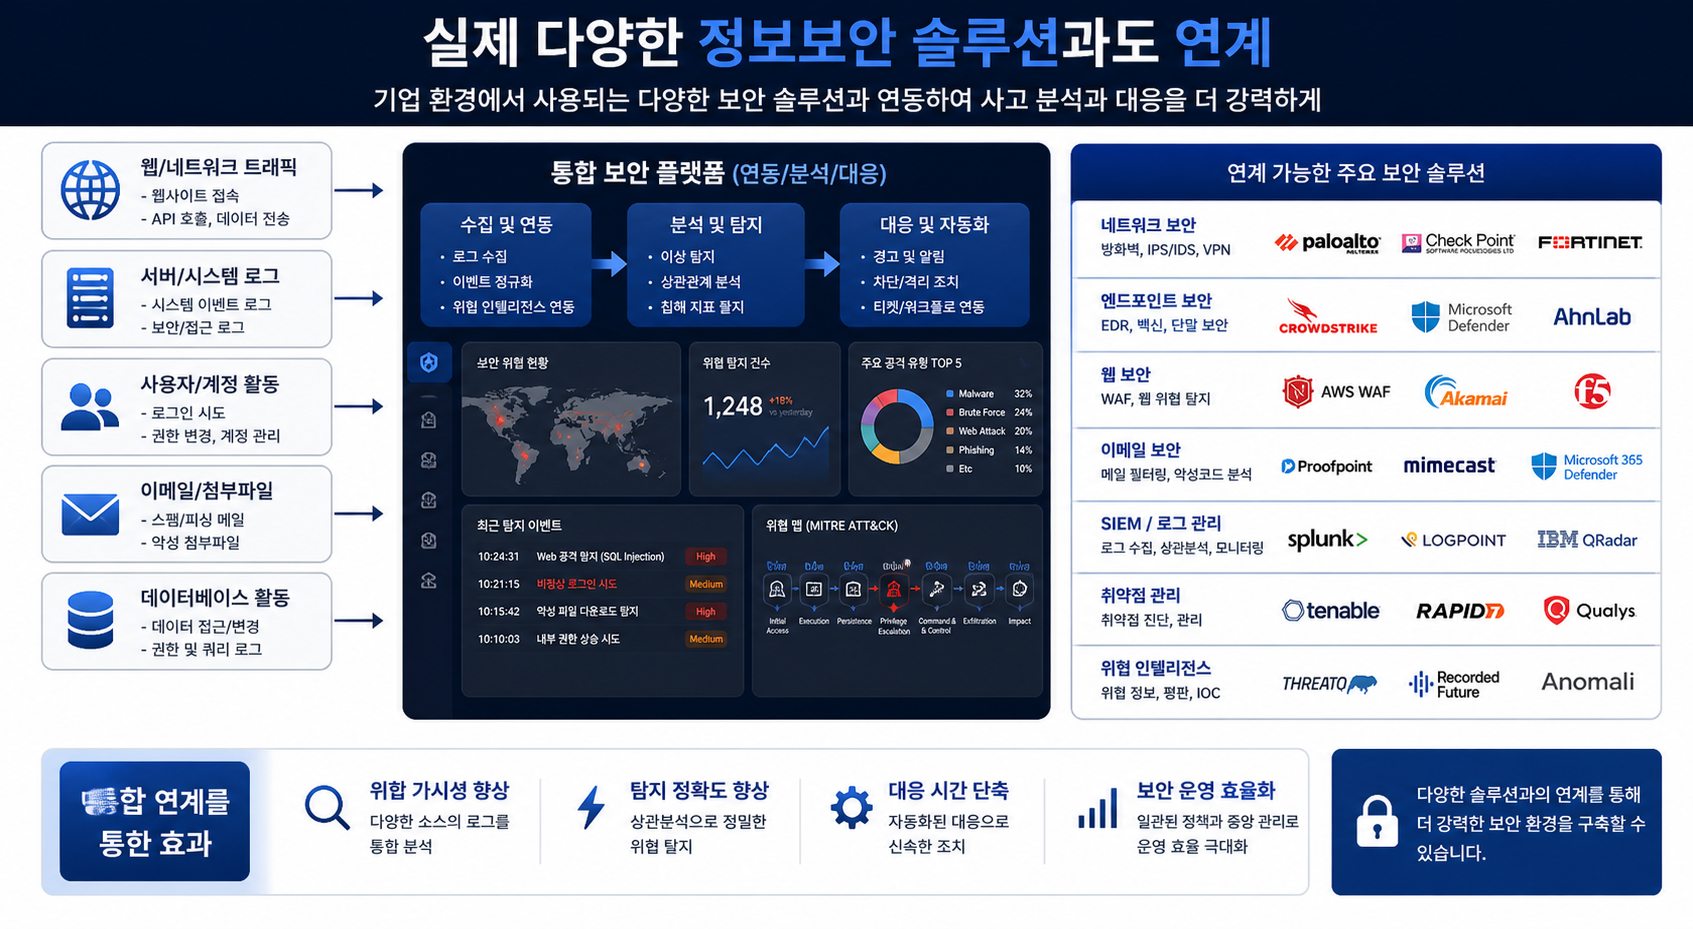
The content covered in this course is primarily utilized in the fields of corporate information security, incident response, network security, web security, security architecture design, IT infrastructure operation, and security education.
Each session is structured in the stages of Problem Situation → Cause Analysis → Solution and Application, with all procedures from incident risk types to resolution organized in a scenario format.
Operating System and Version (OS): OS types and versions such as Windows, macOS, Linux, Ubuntu, Android, iOS, etc.
Tools used: Software/hardware versions required for practice, billing plans, whether virtual machines are used, etc.
PC Specifications: Recommended specifications for running programs, such as CPU, memory, disk, graphics card, etc.
Format of the provided learning materials (PPT, cloud links, text, source code, assets, programs, example problems, etc.)
Quantity and capacity, characteristics of other learning materials, and precautions, etc.
Whether essential prior knowledge is required, considering the learning difficulty level
Content directly related to taking the course, such as lecture video quality (audio/video), and recommended learning methods
Information regarding Q&A and future updates
Notice regarding copyrights of lectures and learning materials
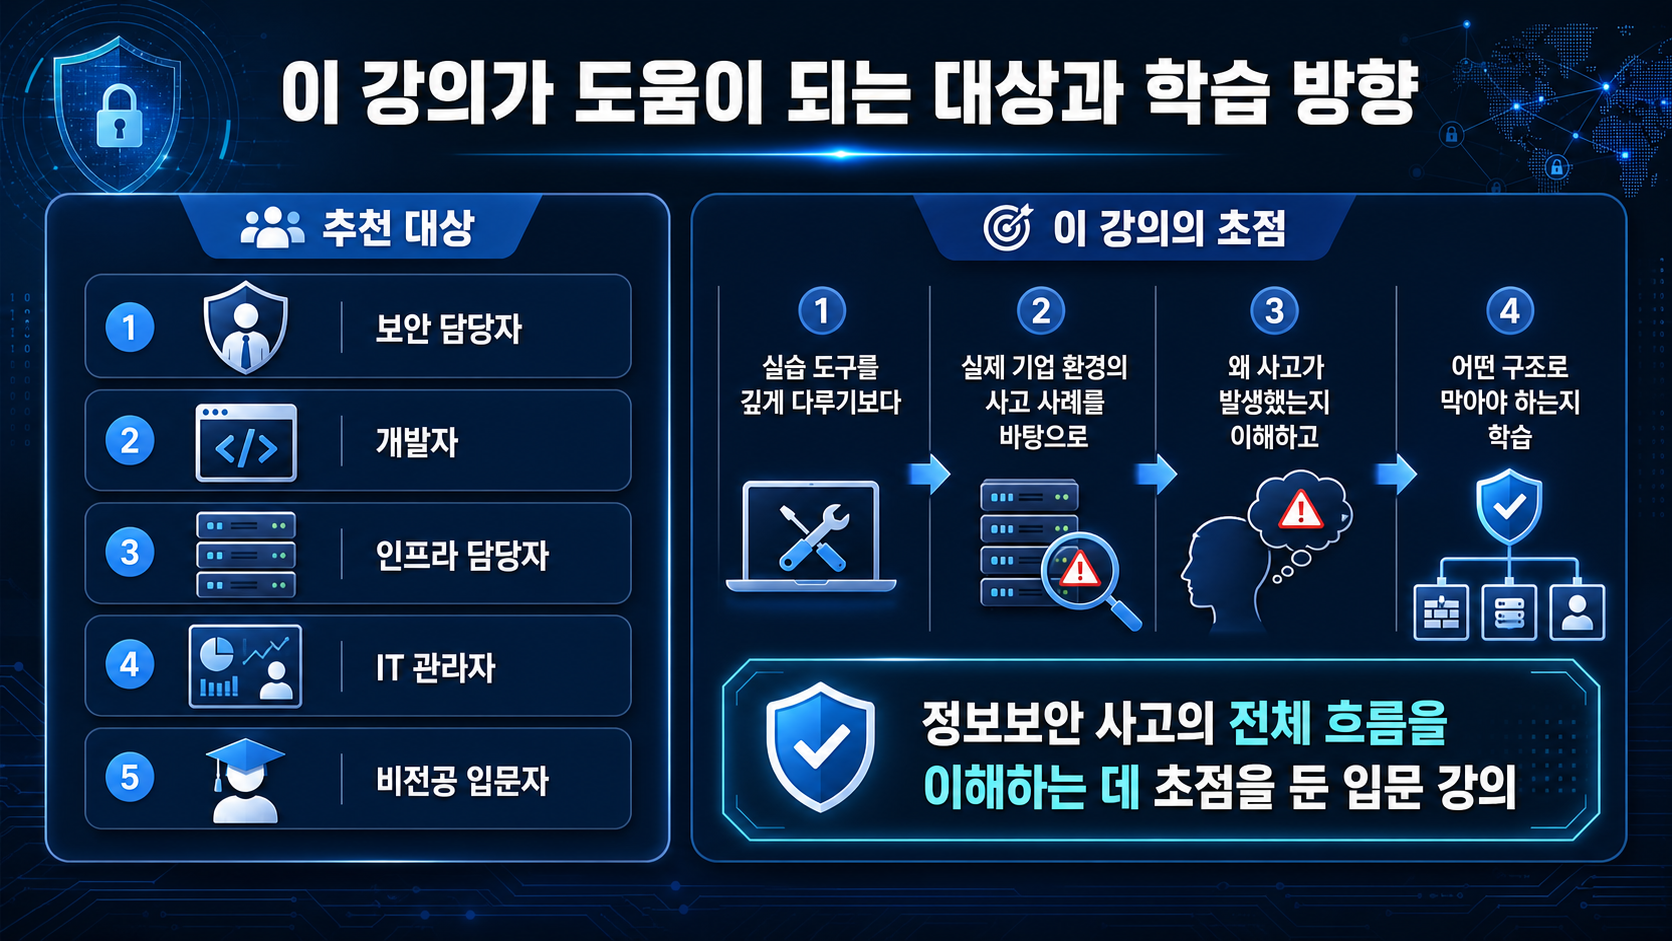
Who is this course right for?
A beginner learning information security for the first time
Developers and Infrastructure Managers
Entry-level corporate security professional
IT Practitioners and Managers
Non-majors who want to learn security incident response concepts
All employees subject to security training
Need to know before starting?
Understanding basic IT terminology
Basic understanding of web service architecture
Basic Concepts of Information Security
Basic sense of corporate IT environments

Hello.
I’m Byte Detective.
I have worked in the fields of IT strategy and information security for over 24 years in the AI and IT sectors. Currently, I create and develop e-learning content needed in the AI era, work as an external instructor (including at MultiCampus), and provide AI and IT-related consulting services to small and medium-sized enterprises.
Based on this practical work experience, upgrade your knowledge and skills with clear, easy-to-understand, and engaging courses that will genuinely help you in your day-to-day work.
YouTube channel: https://www.youtube.com/@신동주-s1b
All
21 lectures ∙ (6hr 25min)
Course Materials:
1. Intro
02:35
All
4 reviews
4.8
4 reviews

Reviews 3
∙
Average Rating 4.7
Reviews 134
∙
Average Rating 5.0
5
===== 26/06/03/Wed 13:35 ===== I have gained a great understanding of security through the lectures categorized by information security types. Thank you for creating such a great course.
I hope this lecture was very helpful to you. I will continue to repay your support with even better lectures in the future. In particular, OT security is very closely related to industrial security. For your information, if you are interested in OT security, I recommend preparing for the state-certified Industrial Security Manager certification. If you are interested in this certification, I will send you a discount coupon so that you can take the Industrial Security Manager course available on Inflearn. Thank you.
Reviews 2
∙
Average Rating 5.0
Reviews 4
∙
Average Rating 4.5
Explore other courses in the same field!