2026 ISMS-P Certification Standards Special Lecture (Revised)
ISMS-P WIN

We are revealing the know-how for selecting certification criteria, which accounts for 60% of the ISMS-P certification auditor exam.

Basic
ISMS-P
KCA Information Security Risk Manager (ISRM) certification course! The cornerstone for acquiring the top 3 personal information protection certifications: CPPG, ISMS-P!
21 learners
Level Beginner
Course period 6 months
Information Security Risk Management Methods
Information Security and Personal Information Protection Affairs
Privacy Impact Assessment
This is a theoretical lecture that will help you obtain ISRM certification.
Engineer Chang-Joong Kim, who has proven the highest passing rate in ISMS-P and CPPG lectures, guides you through passing the ISRM exam.
The lecture is given directly by the author who wrote and lectured on the best-selling ISRM attic textbook.
Anyone who really wants to obtain ISRM certification
Anyone who really wants to obtain ISRM certification
For those who want to acquire practical knowledge through special lectures on ISMS-P, access control, and information protection systems

Those who will grow into information security leaders by improving their information protection expertise
Anyone who wants to learn information security practices from instructors with CISO and CPO experience
Anyone who wants to perform a role as a PM or team leader as an information security project expert

Those who want to improve their work performance by systematically learning information security work
Those who want to systematically learn about information security concepts, systems, life cycles, and protection measures.
Those who want to advance to become experts through career development, promotion, and job change

You can most certainly pass the ISRM exam to obtain the certificate.
Based on what you learned in this lecture, you will be able to explain information security work well to your colleagues and juniors.
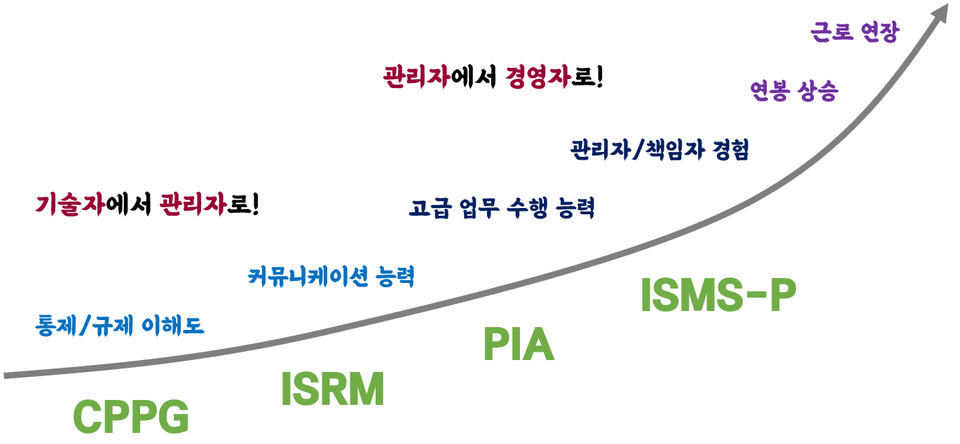
It can be an opportunity to develop your career from a security technician to a manager, or from a manager to a director.
Starting with ISRM, becoming a security expert through ISMS-P, CPPG (Personal Information Manager), and Information Security Engineer
Unparalleled test coverage
The ISRM course covers a very wide range of exams. You must understand the basics of information security risk management and the laws and regulations of information security. In order to ensure that you pass the exam, we have organized special lectures on information security systems, ISMS-P certification criteria 2, and access control.
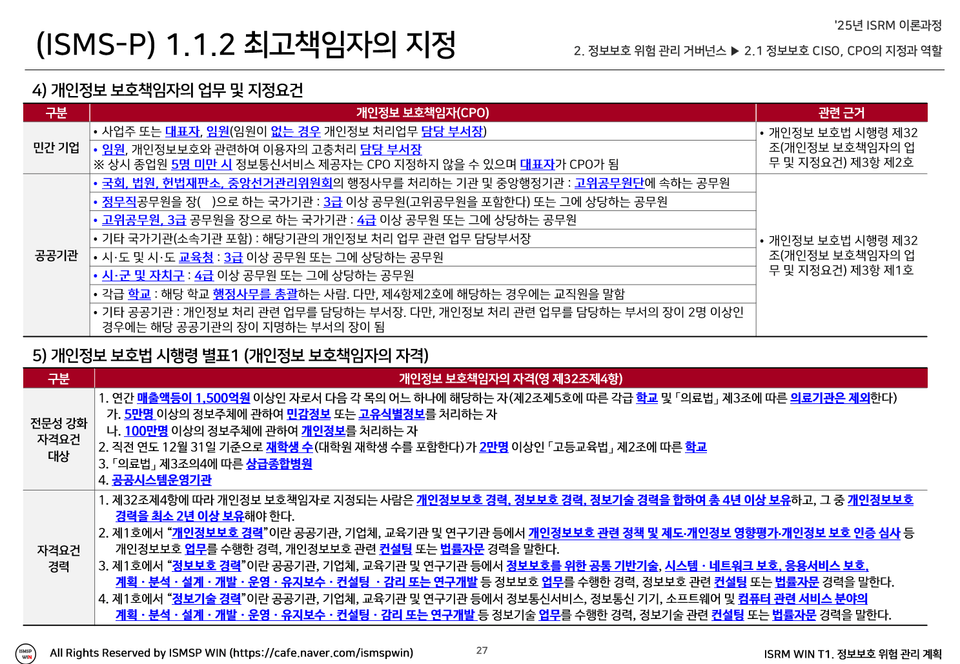
Key strengths of this course
We provide the most systematically organized learning materials in conjunction with the ISMS-P certification. You can learn with integrated thinking rather than learning fragmentary concepts, systems, laws, and regulations.
T1. Information security risk management plan, T4. Information security management system operation
[ 0. Orientation ]
[ 1. Understanding Information Security Management ]
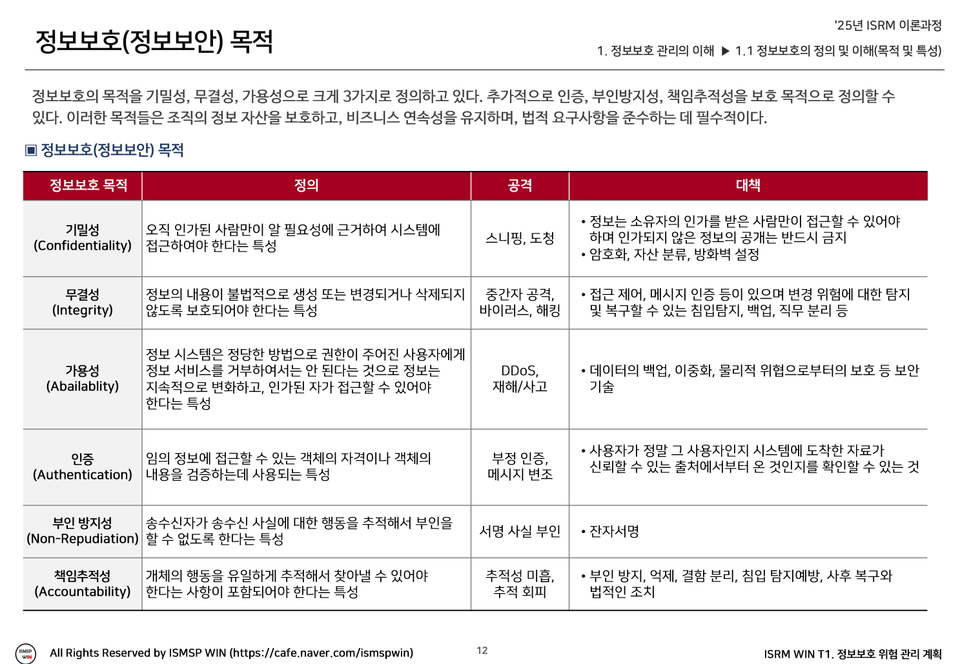
1.1 Definition and understanding of information security (purpose and characteristics)
1.2 Selecting the protection targets that the organization must comply with legally
1.3 Identifying the information protection requirements of the protected object
[ 2. Information Security Risk Management Governance ]
2.1 Designation and Role of Information Security CISO and CPO
2.2 Establishing a decision-making system (budget, organization) for CISO and CPO
2.3 Establishing information security plans, risk management, and protection measures
[ 3. Establishment of information security management system (life cycle) ]
3.1 Establishing the organization's information security policy and related implementation regulations
3.2 Establishing an information security organization (CISO, CPO, committee, security team)
3.3 Check compliance with information protection laws and policies
T2. Information security risk assessment, T4. Information security management system operation
[ 01 Selection and preparation of risk management assessment methodology ]
1.1 Definition, classification and selection of risk assessment methods
[ 02 Information Security Risk Assessment ]
2.1 Identification of information assets and assessment of importance
2.2 Threat classification, identification and assessment of likelihood of occurrence, etc.
2.3 Vulnerability Identification and Assessment
2.4 Identifying and Assessing Legal Compliance
2.5 Comprehensive risk assessment and target risk level assessment
T3 Information Security Risk Response, T5. Information Security Risk Countermeasure Management
[ 01 Implementation of protective measures ]
1.1 Establishing a management strategy and protective measures for identified risks
1.2 Considerations when implementing protective measures
1.3 Check the implementation of the protection measures after completion
[ 02 Protection measures applicable to information and communication service providers ]
2.1 Overview of laws and systems applicable to information and communication service providers
2.2 Compliance with legal requirements for information and communication service providers
2.3 Compliance System for Information and Communication Service Providers
[ 03 Personal information processor/credit information provider application protection measures ]
3.1 Overview of laws and systems applicable to personal information processors/credit information providers
3.2 Personal information processor/credit information provider compliance legal requirements
3.3 Personal information processor/credit information provider compliance system
[ 04 Information Security Industry Application Protection Measures ]
4.1 Overview of laws and systems applicable to the information security industry
4.2 Information Security Industry Compliance Legal Requirements
4.3 Information Security Industry Compliance System
ISMS Pwin Instructor Kim Chang-joong
For the past seven years, we have been researching, analyzing, and publishing to help candidates obtain their personal information protection certification.
I have worked as a personal information protection consultant at large corporations and have held the roles of Chief Privacy Officer (CPO) and Chief Information Security Officer (CISO).
It was produced with reference to the KCA ISRM guide, KISA guide, and papers.
ㅇ Career History
- Current A Company Information Security Office Director (CISO, CPO)
- Former LF Chief Information Security Officer (CISO)
- Currently completing a Ph.D. in Industrial Engineering from the Graduate School of IT Policy at Seoul National University of Science and Technology
- Current public institution interviewer and proposal evaluation committee member (KISA, Korea Information Society Agency, etc.)
- Former LG CNS Personal Information Protection Consultant
ㅇ Teaching experience
- Infolever Consulting Personal Information Protection Management System Auditor Training Course 10 times
- Lectures on personal information protection and safe use of personal information for public institutions and private companies
- Lectures on cloud security, how to obtain IT certifications, etc.
O writing
- Pass the ISMS-P Certification Examiner Qualification Test in One Book (Crown Publishing)
- ISMS-P Qualification Test Practice Test (Crown Publishing)
ㅇ Qualification of possession
- Information Management Technician, ISMS-P, PIA, CPPG, Information Security Engineer, PMP, etc.
o External activities
- ISMS-P certification auditor, ISO27001 certification auditor, ClSSP, etc.
- ISMS-P Pass Cafe Master (http://cafe.naver.com/ismspwin )
- ISMS-P Youtube channel operation ( https://inf.run/GJcv7 )
Before taking the class, write down at least three questions and answers that potential students may have.
We encourage answers that reveal the personality of the knowledge sharer rather than obvious or formal answers.
Q. What are the qualifications for ISRM certification?
A 4-year college graduate (or expected graduate) and equivalent experience are required.
Q. Is there anything I need to prepare when watching the lecture?
Devices to view lectures (PC, tablet), lecture notes, and writing tools.
You can take notes on the printed lesson materials and watch the video lectures.
Usually, you will gradually understand it more accurately after listening to the lecture more than twice.
Q. How do I ask questions about the lecture content?
For questions related to taking the course, please post them on the Inflearn bulletin board. For information on the course content, please visit the Inflearn bulletin board.
https://cafe.naver.com/isrmwin
You can post a question on the 'Questions' bulletin board in the cafe.
The learning materials provided are in the format of (PDF electronic file) and unauthorized sharing or distribution is prohibited.
If you print the lecture notes in double-sided printing mode, you can view them like a book.
This course does not provide paper textbooks.
This course is a theoretical lecture course and not a problem-solving course.
If you work hard, you don't need player knowledge.
Having a CPPG certification and an Information Security Engineer certification may be a slight advantage.
We do not provide separate paper booklets other than the electronic file textbooks.
The copyright of the lectures and learning materials belongs to ISMS Pwin (CEO Instructor Chang-Joong Kim).
Who is this course right for?
Those who wish to obtain the ISRM certification
For those who want to become ISMS-P auditors
Need to know before starting?
No prior knowledge is required, but basic knowledge of information security is helpful.

Inflearn Verified
1,323
Learners
203
Reviews
31
Answers
4.6
Rating
13
Courses
ㅇCareer History
- Current lead instructor at ISMSPWIN Co., Ltd.
- Former Chief Information Security Officer (CISO) and Head of the Information Security Team at LF
- Currently has completed doctoral coursework in Industrial Engineering at the Graduate School of IT Policy, Seoul National University of Science and Technology
- Currently serves as an interviewer and proposal evaluation committee member for public institutions (KISA, National Information Society Agency, etc.)
- Former privacy consultant at LG CNS
ㅇLecture Experience
- 10 sessions of the Inforever Consulting Personal Information Management System Auditor Training Course
- Lectures on personal information protection and the safe use of personal information for public institutions and private companies
- Lectures on cloud security and how to obtain IT certifications, among other topics
Authored Works
- Pass the ISMS-P Certification Auditor Qualification Exam with One Book (Crown Publishing)
- ISMS-P Qualification Exam Practice Mock Tests (Crown Publishing)
ㅇ Certifications held
- Professional Engineer of Information Management, ISMS-P, PIA, Information Security Engineer, PMP, etc.
External Activities
- ISMS-P Certification Auditor, ISO 27001 Certification Auditor, CISSP, etc.
- Master of the ISMS-P Pass Cafe (http://cafe.naver.com/ismspwin)
- Operates the ISMS-P YouTube channel (www.youtube.com/ismspwin)
All
64 lectures ∙ (39hr 11min)
Course Materials:
All
4 reviews
4.8
4 reviews

Reviews 4
∙
Average Rating 5.0
Edited
Reviews 1
∙
Average Rating 5.0
Reviews 1
∙
Average Rating 4.0
Edited
Reviews 3
∙
Average Rating 4.7
Check out other courses by the instructor!
Explore other courses in the same field!